

Card Tokenization Explained: How India Secures Your Card Data
Card tokenization replaced stored card numbers with safe substitutes. Here's how it works, and why RBI made it mandatory in India.
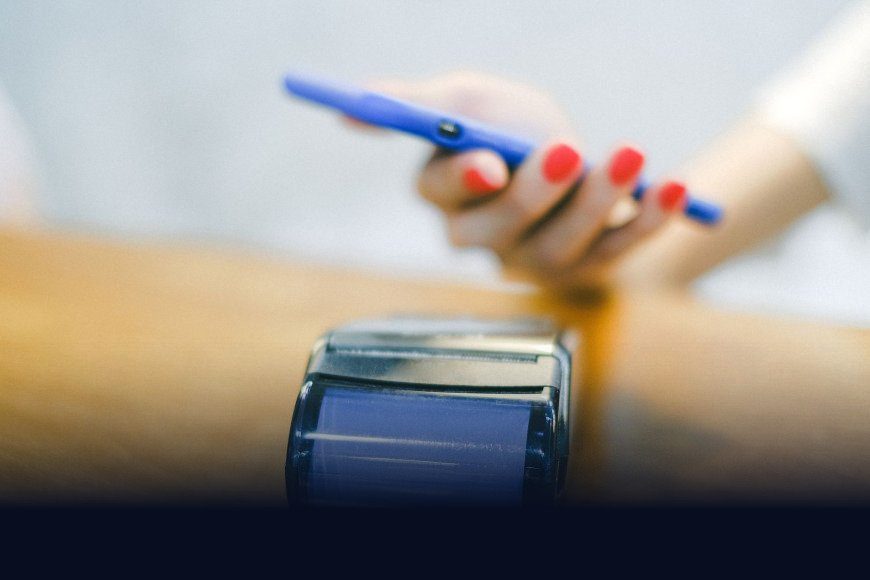
Ever notice how most Indian shopping apps stopped showing your full card number a while back, and instead show something like "XXXX XXXX XXXX 4521, tap to pay with saved card"? That's not a UI tweak. It's tokenization, and it's the reason your card details are harder to steal than they used to be, even if a shopping app gets hacked.
Here's the problem tokenization was built to solve. For years, Indian e-commerce sites and apps routinely stored your actual 16-digit card number, expiry date, and sometimes even the CVV (the three-digit security code on the back of your card) on their own servers, so you wouldn't have to type them in every time. Convenient, yes. But every one of those servers became a juicy target. If a food delivery app or a small online retailer got breached, your real card number could end up for sale on the dark web, the hidden part of the internet where stolen data gets traded.
What tokenization actually does
Tokenization replaces your real card number with a randomly generated substitute, called a token, that's unique to that specific device, app, and merchant (the business you're paying). The token looks like a card number but it's useless anywhere else. If a hacker steals a database full of tokens, they get nothing they can actually use to make a purchase elsewhere, because each token is locked to one app-device combination and processed through your card network (Visa, Mastercard, RuPay, and so on), not the merchant directly.
This is a genuinely different idea from encryption, which is the other security term people often mix it up with. Encryption scrambles your real card data into unreadable code that can still, in principle, be unscrambled with the right key. Tokenization doesn't scramble anything reversible on the merchant's end at all, it hands the merchant a stand-in value that was never mathematically derived from your actual card number in a way they can reverse. The real number lives only with your bank and card network.
Your card number never actually touches the merchant's servers anymore, it just leaves behind a stand-in that's worthless to anyone who steals it.
Why Indian shoppers had to relearn how to pay online
This isn't a feature some app rolled out quietly. The Reserve Bank of India (RBI), the country's central bank and the body that regulates how digital payments work here, mandated card-on-file tokenization for every merchant doing business in India starting in 2022. Companies were barred from storing raw card numbers and CVVs past a short transaction window. That's exactly why millions of Indians suddenly had to re-save their cards across every app, from Swiggy to Amazon to BookMyShow, around the same time, and why that "add new card" screen became oddly familiar for a few months.
The RBI's logic was straightforward: with online fraud and data leaks rising across Indian e-commerce and fintech platforms, the biggest risk wasn't the payment moment itself, it was the pile of stored card numbers sitting on merchant servers long after the transaction was over. Removing that pile removes the target. For a country where UPI and card payments now handle a huge share of daily commerce, this single rule change quietly tightened security for practically every digital transaction in India.
What this means day to day
In practice, here's what changed for anyone shopping online in India:
- You tokenize a card separately for each app or website, so "saving" your card on Myntra and on Zomato creates two different tokens, not one shared record.
- If you lose your phone or an app gets compromised, the exposure is limited to whatever that one token can do, not your entire card.
- Switching phones can mean re-tokenizing your cards, since tokens are often tied to the specific device.
- Your bank, not the shopping app, remains the only party that can map a token back to your real card number.
Worth knowing: tokenization protects stored card data, but it isn't the only layer standing between you and fraud. Phishing messages that trick you into typing your card details directly, or OTP scams where someone convinces you to read out the one-time password sent to your phone, bypass tokenization entirely because you're the one handing over the information. The technology protects what merchants store, not what you choose to type into a fake link.
The practical takeaway
If you've been mildly annoyed at having to re-enter card details more often than you used to, that friction is doing real work. Every time an app can't just keep your raw card number lying around, that's one less database breach away from your money being at risk. The next time a payment screen asks you to tokenize a card instead of just saving it, it's worth taking the extra ten seconds, because that small inconvenience is quietly one of the better consumer protections to come out of Indian fintech regulation in recent years.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0