


F5 BIG-IP Zero-Day Lets Hackers Break In Without a Password
A critical F5 BIG-IP flaw is already under attack with no login needed — here's what Indian firms running it should do right now.
Attackers didn't wait for a patch. By the time F5 published its advisory on September 22, hackers were already using the flaw to run their own code on BIG-IP boxes — no username, no password, just the right request sent to the right server.
What Actually Broke
The bug is tracked as CVE-2026-94127, and it carries a CVSS score of 9.8 out of 10 — the industry's standard severity scale, where anything past 9 is about as bad as a flaw gets. It's a heap-based buffer overflow, a class of bug where a program writes more data into a chunk of memory than that chunk was sized to hold, letting an attacker overwrite nearby memory and eventually hijack what the program executes next. In this case it sits inside F5's Access Policy Manager, or APM, the module that big organizations use to control who gets into their internal apps and VPNs.
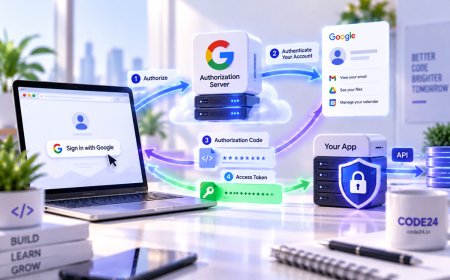
The catch that makes this a genuinely bad one: it's unauthenticated remote code execution, or RCE — meaning an attacker who can merely reach the affected server over the network, with no valid login of any kind, can end up running arbitrary commands on it. F5 says exploitation needs a specific setup — a BIG-IP virtual server with both an APM access policy and an OAuth profile configured together. OAuth is the standard that lets you log into one app using credentials from another, the tech behind every "Sign in with Google" style button — so it's not every BIG-IP box on the internet. But OAuth-fronted APM deployments are exactly the kind of setup large enterprises lean on for single sign-on into internal tools, which means the boxes that are exposed tend to be sitting at the front door of some fairly important infrastructure.
Why This One Is Different From the Usual Patch Tuesday
F5 didn't find this through routine testing — it found out because someone had already weaponized it. That ordering matters. A vulnerability disclosed alongside a patch, with no evidence of exploitation, gives defenders a head start. A vulnerability disclosed because it's already being used in the wild means every unpatched, internet-facing box has been running on borrowed time since before anyone outside the attackers knew it existed. F5 has shipped hotfixes across its 21.1.0, 17.5.0 and 17.1.0 release trains, but a hotfix only helps once someone actually applies it.
No login. No phishing email. No user has to click anything. Just a crafted request to a box that's supposed to be the thing standing between the internet and your internal network.
Code24 has tracked a steady run of this exact pattern through 2026 — flaws surfacing already-exploited rather than pre-emptively patched, including a Pixel modem zero-day Google disclosed under active attack earlier this month. The common thread is that the gap between "this bug exists" and "someone is using it" keeps shrinking, which leaves less room for organizations that patch on a monthly or quarterly cycle.
What This Means for Indian Organizations
F5 BIG-IP isn't a niche product here. Indian banks, NBFCs, insurers and large enterprises use it widely to manage employee VPN access and to front internal applications with single sign-on — precisely the APM-plus-OAuth combination this bug targets. A successful hit on one of these boxes doesn't just compromise a web server; it potentially hands an attacker a foothold inside the network that staff use to reach core banking and internal systems, which is a different order of problem for regulators than a defaced website. CERT-In, India's nodal cybersecurity agency, routinely issues advisories on exactly this class of vulnerability, but as with most disclosures, applying the fix is left to each organization's own IT team — there's no forced patch clock the way there is in some other markets. For security chiefs (CISOs — the executives who own this decision) at RBI-regulated entities in particular, this is the kind of bug that warrants an out-of-cycle emergency change window rather than sitting in next month's patch queue.
What To Actually Do
- Check whether your BIG-IP deployment runs an APM access policy combined with an OAuth profile — that's the specific combination F5 says is exploitable.
- Apply the relevant hotfix for your release train (21.1.0, 17.5.0 or 17.1.0) immediately rather than waiting for a routine maintenance window.
- If you can't patch right away, restrict network access to the affected virtual servers to trusted IP ranges as a stopgap.
- Review access and application logs on exposed BIG-IP instances for unusual requests to APM/OAuth endpoints going back to early September, given the delay between exploitation and disclosure.
The uncomfortable pattern here isn't really about F5 specifically — it's about how often the products enterprises trust to keep attackers out are themselves turning into the entry point. A firewall, a VPN gateway, an access manager: each one is supposed to be the hardened perimeter, and each one is now a favorite target precisely because a single working exploit against it can unlock everything sitting behind it. Patching this particular hole matters, but the bigger question — how much blind trust any organization places in a single vendor's box at its network's edge — isn't one a hotfix answers.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0