

Dell CSM Bugs Let Attackers Steal Storage Admin Credentials
Dell patched five max-severity flaws in its Container Storage Modules, two scoring a perfect 10/10, that exposed admin access on Kubernetes storage.
If your company runs Kubernetes on top of Dell storage hardware, the patch notes that landed in early October weren't the usual bug-fix housekeeping. Dell confirmed five flaws in its Container Storage Modules software, two of them scoring a perfect 10 out of 10 on CVSS, the standard 0-10 scale security researchers use to rate how bad a bug is — a 10 means it needs zero skill and zero luck to exploit.
What actually broke
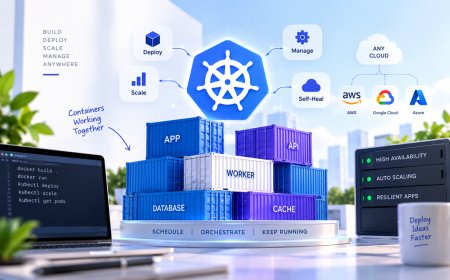
Container Storage Modules, or CSM, is the glue software that lets a Kubernetes cluster talk to Dell's enterprise storage arrays — the systems that actually hold the data behind a bank's app, an e-commerce backend, or a hospital's records. CSM doesn't store anything itself; it just handles requests from the cluster and passes them to the storage array, which means it needs to prove who's asking before handing out access. That's exactly where it fell apart.
Two of the five bugs (tracked as CVE-2026-63688 and CVE-2026-63692, a CVE being the standard ID security researchers assign to a specific flaw) turned out to skip authentication entirely in parts of the system. One let anyone who could reach the storage server pull administrator credentials for every connected storage array, no login required. The other let an outsider walk straight into admin-level access through the authorization proxy, and in setups shared across multiple customers or business units, that access could reportedly spill over into storage meant for someone else entirely.
The other three weren't much better. Two involved credentials and signing keys hard-coded into the software itself — meaning anyone who found them in the code (or in Dell's own old setup guides) could forge valid admin tokens. The fifth was a privilege-escalation bug that could hand a low-level user full root access, the highest level of control on a Linux system, on the actual Kubernetes nodes.
Five vulnerabilities, three of them hard-wired into the software's defaults rather than hidden in obscure edge cases — that's not a coding slip, that's a design that trusted too much by default.
Who needs to care, and why it matters here
This isn't a consumer-facing bug; nobody's laptop is at risk. But it lands squarely on the infrastructure that India's banks, fintechs, and the hundreds of Global Capability Centres run by multinational firms out of Bengaluru, Pune, and Hyderabad depend on every day. Dell's storage arrays and Kubernetes together are a default combination in exactly these environments, and a compromised storage backend doesn't just mean downtime — it means the kind of data exposure that triggers mandatory breach reporting under the DPDP Act, India's data protection law. CERT-In, the government's cyber emergency response team, routinely flags vulnerabilities at this severity level in its advisories, and infrastructure teams running CSM should expect it to show up there if it hasn't already.
For anyone who wants the basics on what Kubernetes itself actually does before this makes sense, our earlier explainer covers the fundamentals.
- Dell's fix is version 1.18.0 of CSM — anything older should be treated as exposed.
- Dell is also telling admins to rotate JWT signing secrets (the cryptographic keys used to verify login tokens), especially anyone who followed its older official setup documentation.
- No public reports have confirmed active exploitation yet, which is exactly the window in which patching actually works.
The pattern worth noticing
What's striking isn't just the severity score. It's that four of the five issues trace back to authentication being skipped, hard-coded, or left over from a now-unsupported component rather than a genuine logic error buried deep in the code. That's a recurring theme in enterprise storage and infrastructure software generally: the parts that are supposed to check "should this request even be allowed" get bolted on later, or inherited from an older product line, and nobody revisits them until a researcher or an attacker does.
For IT teams anywhere, including the large outsourcing and cloud operations run out of India, the practical lesson isn't really about Dell specifically. It's that the software sitting between your cluster and your actual data deserves the same scrutiny as the cluster itself — patch it, audit what defaults it shipped with, and don't assume "internal only" software gets a pass on basic login checks.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0