

Hackers Hijacked French Supermarket Fridges, Sparking Fires
Hackers remotely cranked refrigeration units to 50°C at hundreds of French supermarkets, sparking fires — and India's cold chain has the same exposure.
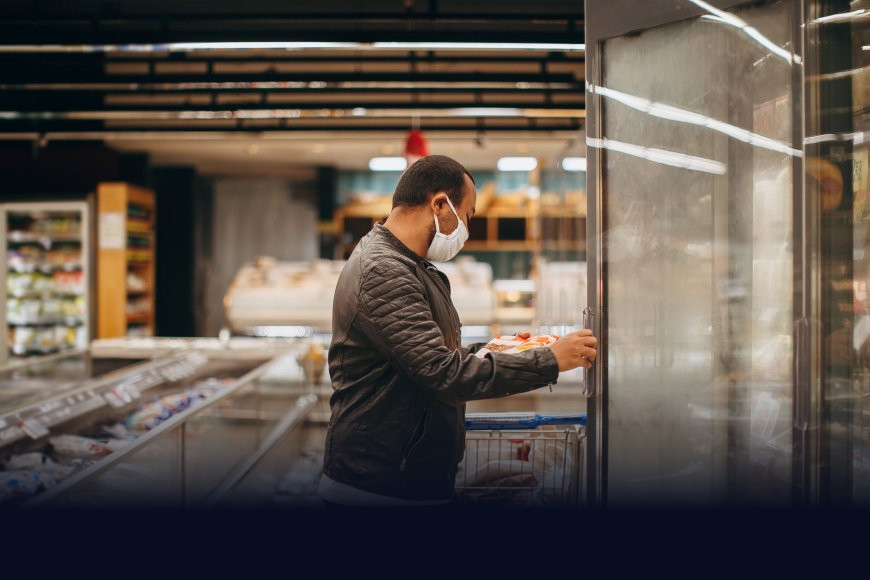
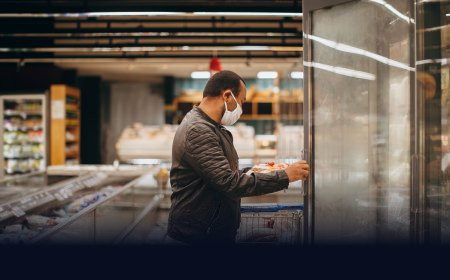
Overnight on October 12th, refrigeration units at as many as 300 supermarkets across France quietly started climbing past 50°C — and nobody in the building had touched a single dial. By morning, chillers had sparked fires, sprinkler systems had flooded aisles, and tonnes of fresh and frozen stock were headed for the bin.
What actually happened
French retail chains including Intermarché, Carrefour, Monoprix, Coopérative U and reportedly some E.Leclerc stores confirmed that attackers had remotely seized control of their store refrigeration systems. Intermarché alone said 150 to 200 of its outlets were affected; Carrefour put its own number at around 80 stores. The attackers didn't steal data or demand a ransom in the usual sense — they simply reset target temperatures on the cooling units to roughly 50°C, hot enough to cook compressors, trip electrical faults, and in several cases start actual fires.
Les Mousquetaires, the group behind Intermarché, estimated losses could run into several million euros once spoiled stock, equipment damage, and fire-related downtime are added up. France's Prime Minister has asked the national cybersecurity agency, ANSSI, to investigate, and the Paris prosecutor's office has opened a separate probe.
How a fridge becomes a weapon
Modern supermarket refrigeration isn't a dumb compressor with a thermostat anymore — it runs on networked industrial controllers (the same category of hardware, often called OT, or "operational technology," that also runs factory floors and power substations) that can be managed remotely over the internet. Security researchers at Claroty's Team82 had already flagged serious flaws in exactly this class of controller, built by Danfoss, months before this attack, and pushed for a firmware update (firmware being the built-in software that tells a device how to behave). Danfoss has said the units hit in France were running outdated firmware, meaning the fix existed before hundreds of stores caught fire — it just hadn't been installed everywhere.
That gap between "patch available" and "patch applied" is where most industrial cyberattacks actually live. Nobody needs a flashy zero-day (a previously unknown, unpatched flaw) when thousands of refrigeration units are still running software from years ago.
"We will have to throw away all of the products" spoiled by the heat, Intermarché told the French news agency AFP, describing the scene inside its affected branches.
Not just a French problem
ANSSI says it's now coordinating with cybersecurity counterparts elsewhere in Europe, since the same refrigeration software is used far beyond France. Reports have linked similar disruptions to:
- Roughly a dozen US military commissaries hit by comparable refrigeration faults in late August
- Stores in Spain, Portugal, Poland, Germany and Belgium reportedly affected around the same period
- Multiple supermarket brands under the same parent groups, suggesting the attackers targeted a shared vendor rather than any single retailer
In other words, this wasn't one store's IT team cutting corners. It was a widely deployed piece of hardware, sold to retailers on several continents, that quietly became a single point of failure.
What it means for India
India doesn't have 300 supermarkets running the exact Danfoss controllers involved in this incident, but it has something arguably more exposed: a fast-growing web of connected cold storage with far less regulatory scrutiny. Quick-commerce dark stores run by Blinkit, Zepto and Swiggy Instamart depend on networked refrigeration to keep produce and dairy moving through same-day delivery. Pharma cold chains carrying temperature-sensitive vaccines and insulin, and large retail chains like Reliance Retail and DMart, increasingly use the same category of internet-connected industrial controllers that failed in France — often from the very same global vendors. Internet of Things (IoT) devices like these rarely get the same patching discipline as laptops or phones, precisely because nobody thinks of a fridge as a security risk until one catches fire. India's CERT-In issues advisories on IoT and OT security, but unlike critical sectors such as power and banking, retail cold-chain infrastructure isn't subject to mandatory security audits — which is exactly the gap that let outdated firmware sit unpatched in France for months.
The bigger lesson
A supermarket fridge was never supposed to be a cybersecurity story. That's precisely the point: the devices least likely to get a security budget are often the ones now wired into the internet by default. Patching firmware on a refrigeration controller is a boring, unglamorous task that nobody wants to prioritize — right up until it's the difference between a routine software update and a warehouse fire.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0